Why Decoding a JWT Is Not Verifying It (And How Security Bugs Slip Through)
Decoding a JWT only unmasks Base64URL strings. Here is how alg: none bypasses, algorithm confusion, and unverified claims slip into production.
Oct 7, 20266 min read
Search for a command to run...
Decoding a JWT only unmasks Base64URL strings. Here is how alg: none bypasses, algorithm confusion, and unverified claims slip into production.
Converting SVGs into custom icon fonts sounds straightforward until you compile your first glyph set. You export ten clean icons from Figma or Illustrator, feed them into an icon font generator, and o
A neatly indented API response can still contain the wrong data. Before treating JSON as trustworthy, separate three questions: does it parse, does it match the expected structure, and does it satisfy
Last Tuesday, a staging auth bug had three devs stumped for half an afternoon. Nginx was spitting 401 Unauthorized. But the tester dumped their Bearer token into Chrome's DevTools console, ran JSON.pa
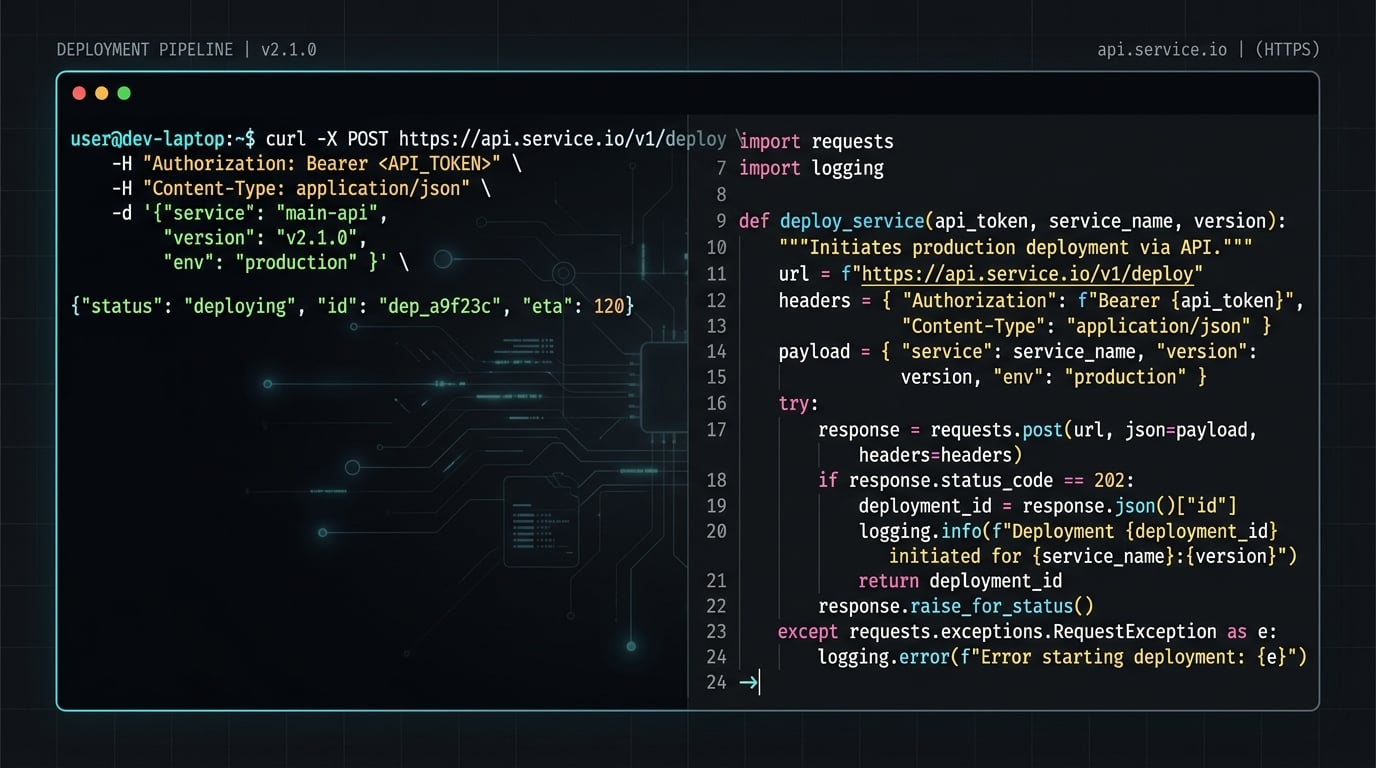
We've all been there: you open Chrome DevTools, click Copy as cURL, paste it into your terminal, and it works like a charm. Then you rewrite it into Python requests or httpx, hit run, and suddenly: HT